
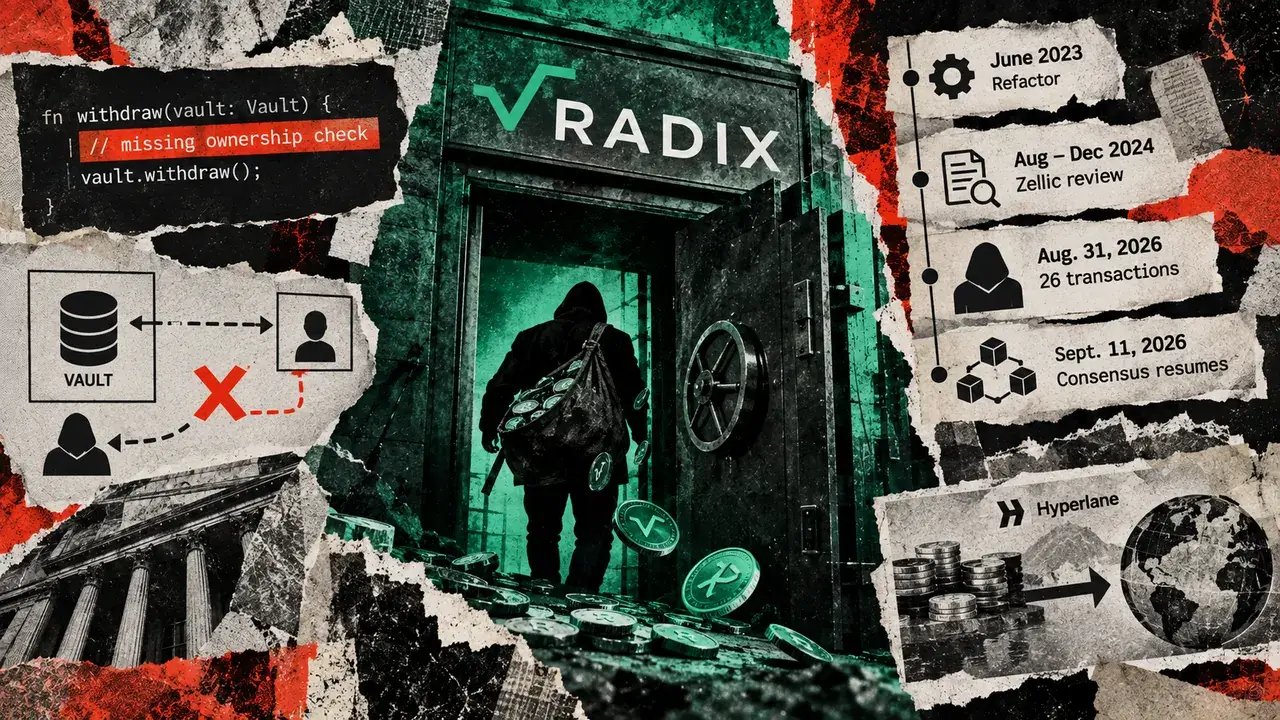
A coding error introduced during a 2023 software clean-up allowed an attacker to steal about $1.3m from the Radix blockchain before validators halted the network to prevent further transactions.
The Radix Foundation said on 17 September that an RDX Works development team introduced the flaw while refactoring the Radix Engine, the software layer responsible for processing transactions and enforcing ownership of assets. The vulnerability went undetected for more than three years and was exploited on 31 August.
Across 26 transactions, the attacker withdrew about 458,915 USDC, 72,420 USDT, 61.08 ETH, 6.35 wrapped Bitcoin, 536.16 SOL and 32.91 BNB, according to a community reconstruction of the ledger. Those assets were worth about $1.26m at market prices on 31 August. A further 13,000 XRD was taken from a vault to cover transaction fees, while the two stablecoins accounted for about $531,335.
The stolen funds were transferred through Hyperlane to Ethereum, BNB Chain and Solana, where they were exchanged for ETH, Radix said. Hyperlane was not compromised: the attacker had already obtained the assets through the Radix Engine, and no private keys were exposed.
The potential impact was significantly wider than the funds taken. Radix investigators found that the vulnerability could have been used against any vault on the network, placing tokens and other assets at risk.
Validators responded by taking enough stake offline to prevent the network from reaching consensus. The decision stopped further transactions from being finalised while developers prepared a fix.
Audit failed to identify authorisation flaw
The defect had also passed an independent security assessment. Zellic reviewed the Radix protocol in 2024, including the engine kernel containing the vulnerable code, but did not identify the authorisation problem.
The flaw affected the way the engine handled vault references. A transaction could specify another user’s vault using its internal address and pass that reference to specially designed smart-contract code. The engine then permitted normal withdrawal functions to run without properly checking ownership.
That meant the attacker could access assets belonging to users, applications and liquidity pools without securing the owners’ signatures.
The Foundation said the 26 exploit transactions took place between 16:02 and 16:57 UTC on 31 August. After investigators established that the problem affected the execution layer rather than one individual application, validators worked together to stop transaction finalisation.
The halt lasted more than 10 days. A protocol update added checks to prevent restricted vault references being used for ordinary withdrawals, and user transactions resumed on 11 September, according to the community ledger reconstruction.
The incident also caused losses in liquidity pools. Removing bridged assets from one side of trading pairs distorted prices, enabling another account to extract millions of XRD from affected pools.
Radix said it would introduce regression tests, improve its security review process and formalise the emergency procedure used by validators to interrupt network activity. The Foundation also said future security work would need to consider increasingly capable AI-assisted code-analysis tools, which it believes may have helped identify the old vulnerability.


